
Latest Quantum Security, PQC, Post-Quantum, Crypto-Agility News
-
Oct- 2026 -29 OctoberQuantum Security & PQC
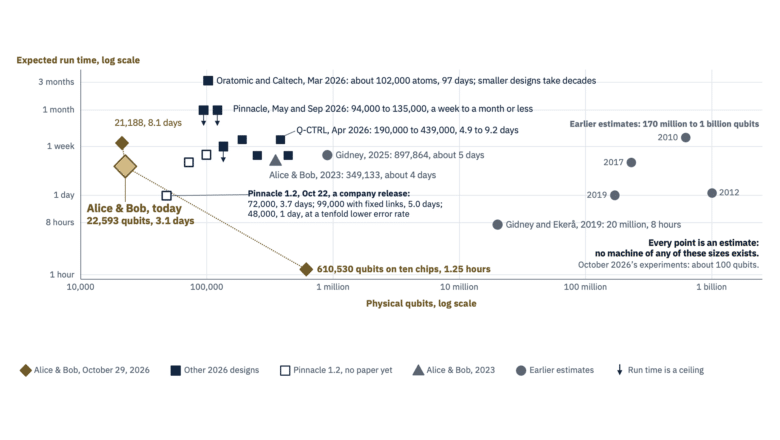
Alice & Bob Estimates 22,593 Qubits Could Break RSA-2048 in Three Days, but Nobody Can Build Those Qubits Yet
Alice & Bob's new estimate puts RSA-2048 at 22,593 cat qubits and 3.14 days, small and fast at once. Here is what that rests on, and a reality check for the headlines it will produce.
Read More » -
28 OctoberQuantum Security & PQC
NIST Finalizes Its Post-Quantum Transition Plan, Deprecating RSA and ECC at All Approved Key Sizes After 2030
In the final version of its post-quantum transition report, NIST added a deprecation step after 2030 for P-256, RSA-3072 and other 128-bit classical parameters. NIST also confirmed that hybrid key exchange can be FIPS 140-validated after 2035.
Read More » -
27 OctoberQuantum Security & PQC
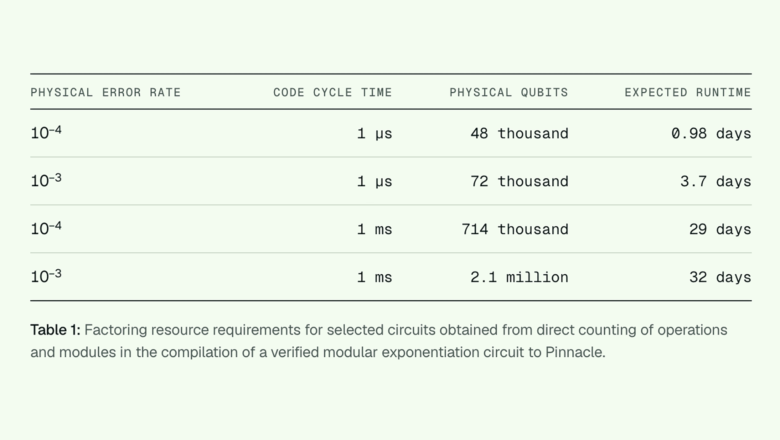
Iceberg Quantum Estimates 72,000 Qubits Could Break RSA-2048 in 3.7 Days but Hasn’t Published the Circuits or the Decoder
In Pinnacle 1.2, Iceberg Quantum reports direct simulations of its logical error rates and cuts its estimated spacetime cost of factoring RSA-2048 about tenfold. The circuits and the Crevasse decoder behind the numbers remain unpublished.
Read More » -
26 OctoberQuantum Security & PQC
Sectigo Reports 38% Have Fully Assessed Their Quantum Exposure, but Only 4% Say Their Certificate Management Is Fully Automated
In its 2026 survey of 500 IT and security leaders, Sectigo reports more quantum assessments and fuller certificate inventories than in 2025. Reading its appendix alongside Chrome's post-quantum certificate plans, I see certificate automation as the work due first.
Read More » -
21 OctoberQuantum Security & PQC

eMudhra CA Keys: A Q-Day Rehearsal at the Scale of One CA
A ceremony error left eight eMudhra intermediate CA keys computable from their certificates for 17 months. Chrome and Firefox blocked them within hours. Linux, runtimes and devices could take years, and a CRQC would expose every classical CA key.
Read More » -
17 OctoberQuantum Security & PQC
MITRE Rated Eight Enterprise Technologies on Post-Quantum Readiness. Key Exchange Is in General Release in Five, Signatures in Two.
In a July review of public evidence, MITRE found no enterprise technology category with FIPS-validated post-quantum support and no post-quantum hardware TPM on sale. What that means for agencies planning toward 2030 and 2031.
Read More » -
17 OctoberQuantum Security & PQC
Starknet Asks Its Stakers Whether to Research Leaving Ethereum Over Quantum Risk
StarkWare says Starknet could finish its post-quantum migration on its own schedule if it left Ethereum. A forum commenter named the cost. One of Starknet's most direct quantum exposures, its users' elliptic-curve keys, does not depend on Ethereum.
Read More » -
17 OctoberQuantum Security & PQC
Coinbase, Which Says It Holds About 12% of All Bitcoin, Sets Out What It Needs From Bitcoin’s Post-Quantum Signatures. Its Request for Multi-Party Signing Is the Hardest to Meet.
On October 13, Coinbase listed what its custody systems need from Bitcoin's post-quantum signatures: multi-party signing, HSM support and a stateless signing mode. The SHRINCS draft already includes the stateless mode. Post-quantum multi-party signing is still a research topic.
Read More » -
15 OctoberQuantum Security & PQC
Germany Sets a 2030 Post-Quantum Target for High-Risk Systems in Government, Business and Critical Infrastructure
BMI, BMDS and BSI have turned the EU's post-quantum roadmap into German guidance. Before 2030 comes an end-2026 checkpoint: named owners, a first cryptographic inventory, and a link to the state-of-the-art duty in the BSI Act.
Read More » -
15 OctoberQuantum Security & PQC
Michael Saylor’s Quantum Claims About Bitcoin, Checked
Strategy's executive chairman says Bitcoin should wait for a quantum threat before upgrading. Its upgrade record, its draft proposals, the arithmetic of block space and his company's own SEC filings all say otherwise.
Read More » -
14 OctoberQuantum Security & PQC
A Key Step of a Quantum Attack on Bitcoin and Ethereum Now Fits in Under 900 Logical Qubits Within Google’s Gate Budget
An open leaderboard now lists secp256k1 point-addition circuits under 900 logical qubits that stay within Google's published Toffoli bound. Whether that saves a quarter of the physical qubits depends on the machine. Nobody has compiled a full attack with them.
Read More » -
13 OctoberQuantum Security & PQC
IonQ Is Buying Elisity for Access to CISOs. Most of the Post-Quantum Capabilities Those CISOs Need First Are Still Missing.
IonQ's hardware acquisitions shorten its own path to better quantum computers. Its security purchases face a different test: whether a CISO planning a post-quantum migration can get inventory, signature migration and validated cryptography from IonQ.
Read More » -
8 OctoberQuantum Security & PQC
Europol Urges Early Action on Quantum Threats to Crypto Wallets and Stored Data
Europol's October 2026 reports place quantum risk on wallet signing keys and long-lived data. Since they were drafted, the IETF has published post-quantum OpenPGP and the hybrid TLS standards behind key exchange already running in major software.
Read More » -
7 OctoberQuantum Security & PQC
US Agencies Had Until May 2023 to Inventory Quantum-Vulnerable Cryptography. Auditors Found One of 24 Inventories Complete.
Washington called the federal inventory of quantum-vulnerable cryptography comprehensive in 2023. An audit made public on October 6 checked the inventories against agencies' own records and asked sampled agencies for evidence. One passed, and most sampled entries had no documentation.
Read More » -
5 OctoberQuantum Security & PQC
Dutch Quantum Strategy Says Prepare for Q-Day Around 2030. Medium-Risk Systems Have Until 2035.
Dutch central-government organizations are asked to move high-risk systems to post-quantum cryptography by the end of 2030 under a new national strategy, which expects a CRQC between 2029 and 2035 and adds no money for the migration.
Read More »


